Audit healthcare code without the cloud.
Hospital systems, EHRs, lab and telehealth apps hold patient data, so their source code should not go to a cloud AI for review. Nadhi Audit reviews it on your own machine, with a model we trained ourselves, and writes a report you can show a regulator.
Apple Silicon · Intel Mac · macOS 12+
One audit, reported against
Finds the weak code
Against the OWASP Top 10 and CWE: hardcoded keys, injection, weak crypto, missing access checks, patient data in logs.
Checks your libraries
Every version your lockfile resolved, matched against a CVE database on your disk.
Writes the report
For HIPAA, DPDP or GDPR, each finding citing its section. A dated PDF for your auditor, fixes on a branch if you want them.
Why healthcare cannot use a cloud AI auditor
Code carries more than code
Config files, logs and test fixtures hold API keys and records that look like patients. Sending the repository to a cloud AI hands all of it to another company.
A cloud reviewer is a new data processor
If that code or its test data can contain patient information, HIPAA needs a business associate agreement and DPDP a processor contract. Many hospitals do not allow it at all.
AI-written code needs more review, not less
Whether your developers wrote it or an AI assistant did, it gets the same OWASP Top 10 and CWE audit, on your own machine.
Three steps
Point it at your code
A folder on your Mac, or a repository you clone once.
It runs on your GPU
Nothing is uploaded. The network is not used during the audit.
You get the report
Every finding names the file, the line and the rule it broke.
The network is used once, to copy the code in. Then it is cut.
What is doing the work
A model we trained ourselves, wrapped in checks that do not trust it.
An agent, not a pattern match
It reads across files, decides whether the control is really missing, writes the patch, then checks its own work.
Our own model, on your GPU
Nadhi_Audit_FT.gguf, fine-tuned by us on security work and agentic tool calling, running on Apple Silicon Metal.
Fixes that are verified twice
The compiler re-parses the patch and the rule that raised the finding is run again. A patch that fails is held back.
Works inside your editor
Type /audit in Claude Code or Cursor. The audit still runs on your machine.
How the model was taught: security findings, and the tool calling an agent needs to act on them.
What it looks for
One pass. Pick the rulebook you have to answer to.
Security
The OWASP Top 10:2025, finalised January 2026. Every finding names the category and the CWE.
Plus the mistakes AI coding assistants tend to make: a secret key that is public because of its name, a database table with no access policy, a package that never existed.
Compliance
Same audit, different report. Each finding cites the section it engages.
§164.308, §164.312, §164.514 and §164.530(j)
Section 8(5), and Rules 6, 7 and 13 with the Third Schedule
Articles 5, 8, 28, 30, 32 and 35
A technical mapping, not a legal opinion. Your counsel still signs it off.
What an audit costs in 2026
Published prices for the conventional route, next to ours.
| Audit | Typical price | How often |
|---|---|---|
| HIPAA security risk assessmentSource: AccountableHQ | $2,000–$10,000 small practice · $20,000–$100,000 mid-size | Once a year |
| GDPR auditSource: Konfirmity | $5,000–$25,000 small · $25,000–$75,000 mid-size | Once a year |
| DPDP Act data auditSource: Consently | ₹1–3 lakh SME · ₹5–10 lakh enterprise | Once a year |
| Web application penetration testSource: Invicti | $4,000–$20,000+ per test | Once or twice a year |
| Enterprise code scanner (SAST), 50 developersSource: Vendr, Snyk | $48,000–$84,000 a year | Every commit |
| Nadhi Audit, Team5 Macs, all four rulebooks, any number of repositories | ₹50,000 a year (about $600) | Every commit |
Every commit, not once a year
An annual assessment is a snapshot. Healthcare code changes every week, and so can the audit.
The code never leaves
No assessor or cloud vendor receives your repository, so there is no new business associate or processor to sign.
Four rulebooks, one licence
OWASP Top 10 / CWE, HIPAA, DPDP and GDPR from the same scan, with fixes that are checked before you see them.
Not a replacement. A HIPAA risk analysis or a GDPR audit also covers policies, staff and physical safeguards, and a penetration test attacks the running system. Nadhi covers the code, all year, so that the yearly assessment finds less. Prices are the sources' published 2026 ranges, checked September 2026.
It has already been used in anger
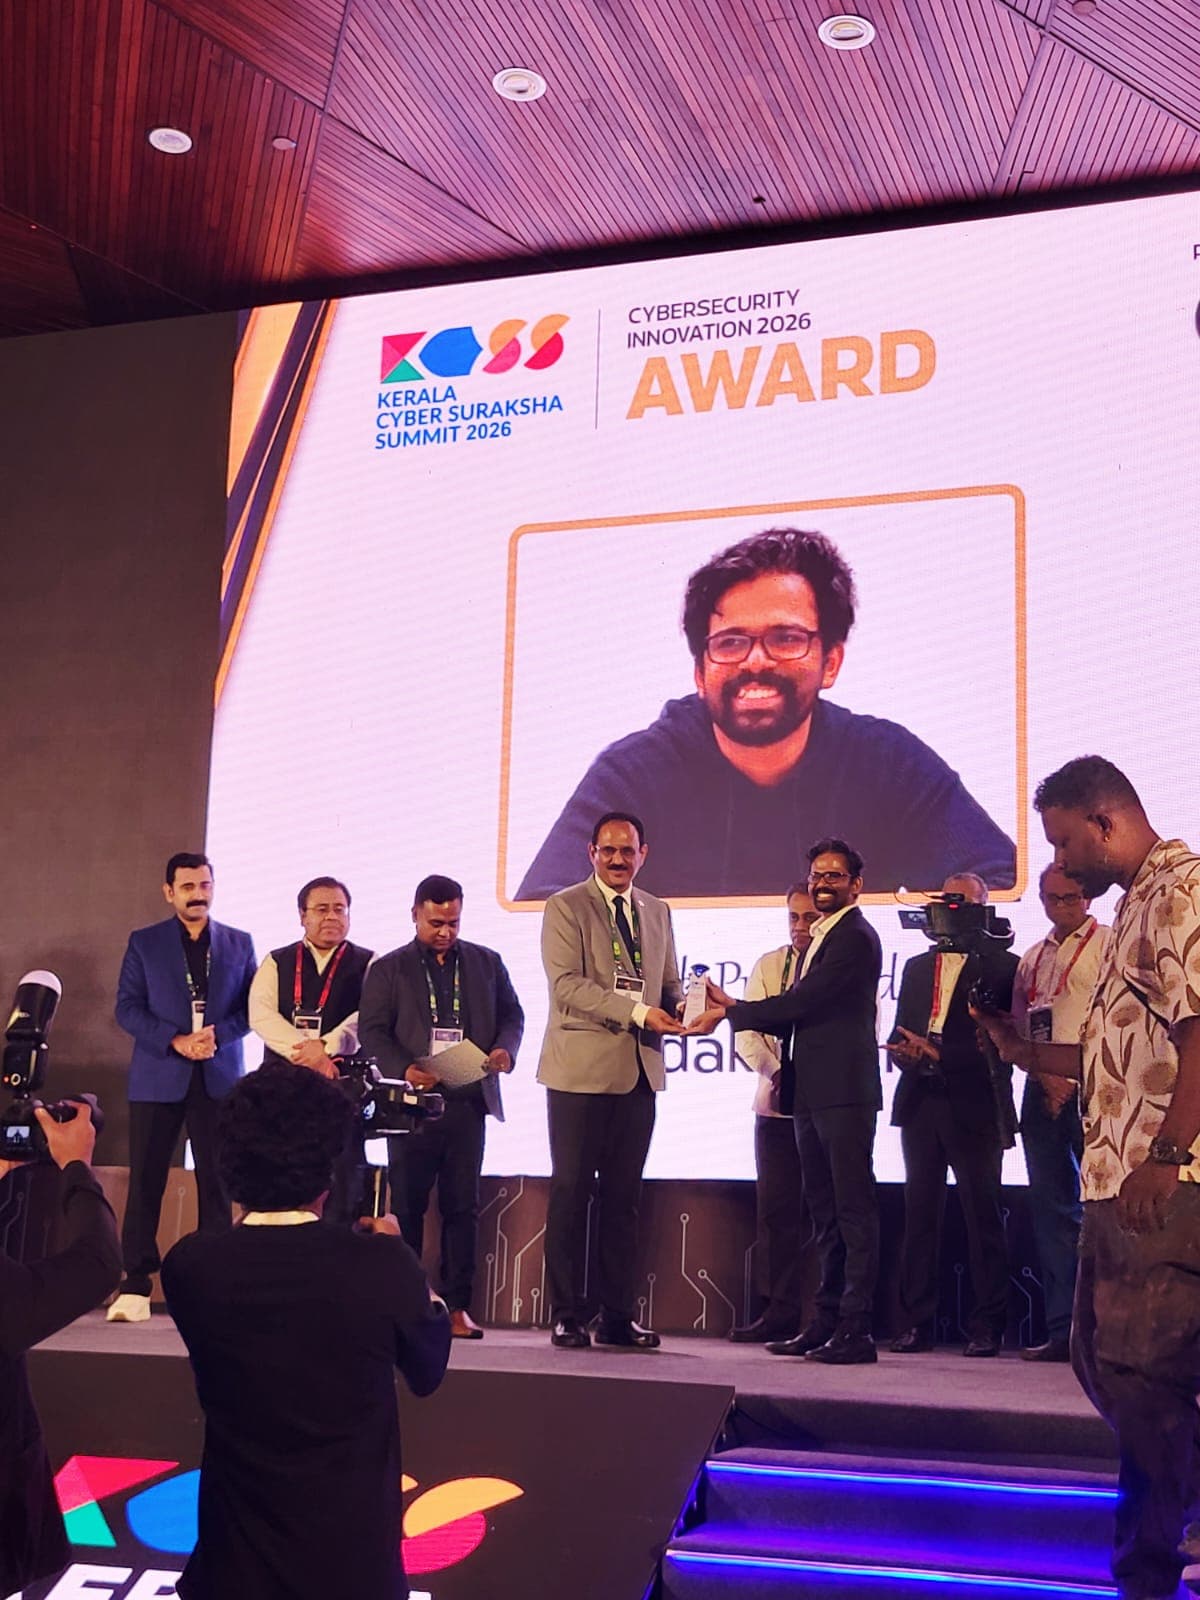
Cybersecurity Innovation Award 2026
Kerala Cyber Suraksha Summit, Kochi, 5 September 2026.
Two fixes now run in hospital software
Merged by the maintainers of Medplum and OpenELIS Global, which runs in labs in more than 25 countries.
Tested on 30 real codebases
71,418 files. Of the library warnings, 99.6 percent were confirmed correct against the public advisory database. See the numbers.
Pricing
Same auditor in every tier. You are only buying more machines.
Billed yearly in rupees. A licence activates on a fixed number of machines, and you can release a machine from your dashboard. It works offline after the first activation.
Need a long-term partner?
Hospitals, health-tech teams and their IT vendors: tell us what you are building and we will work out the rest with you.
Contact usAudit your code tonight
It runs on your Mac. Nothing is uploaded.
Apple Silicon · Intel Mac · macOS 12+